 Innsigle
Walkthrough: Hugo site
You have (or can create) a static site with Hugo. You want a house key in 1Password, public keys under /.well-known/innsigle/, and a signed homepage — without Innsigle learning Hugo’s layout rules.
Screencast
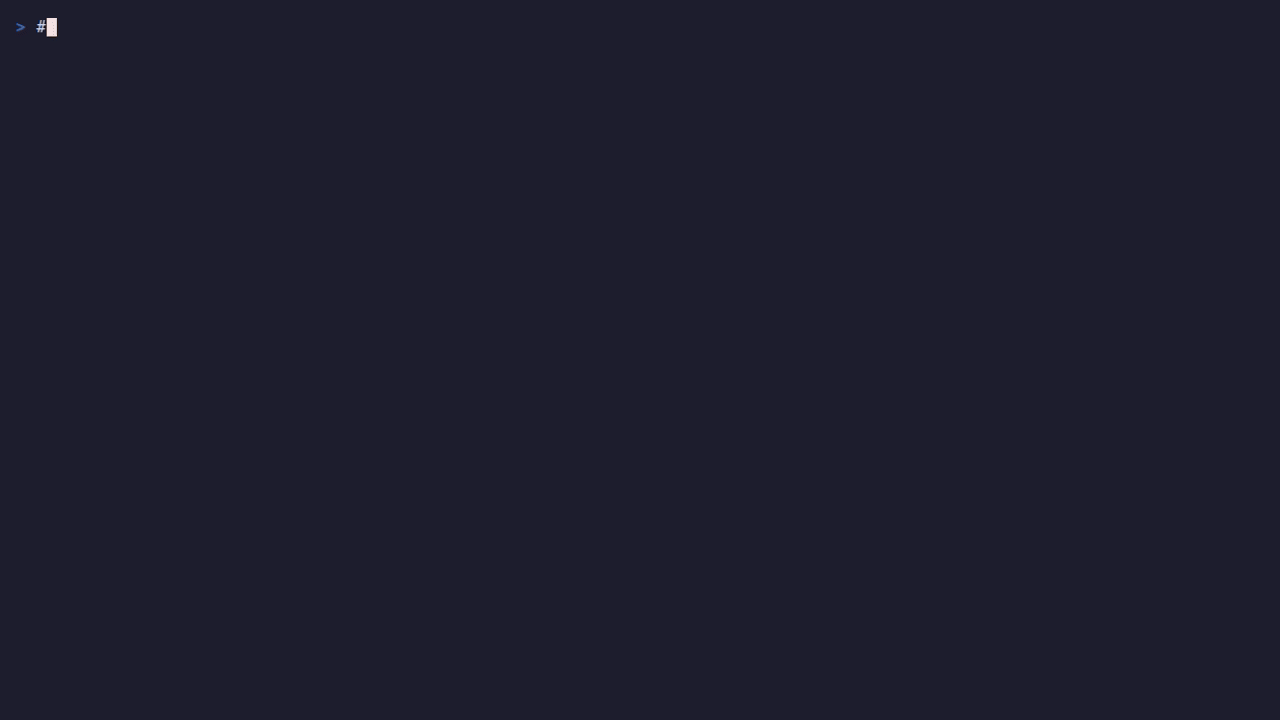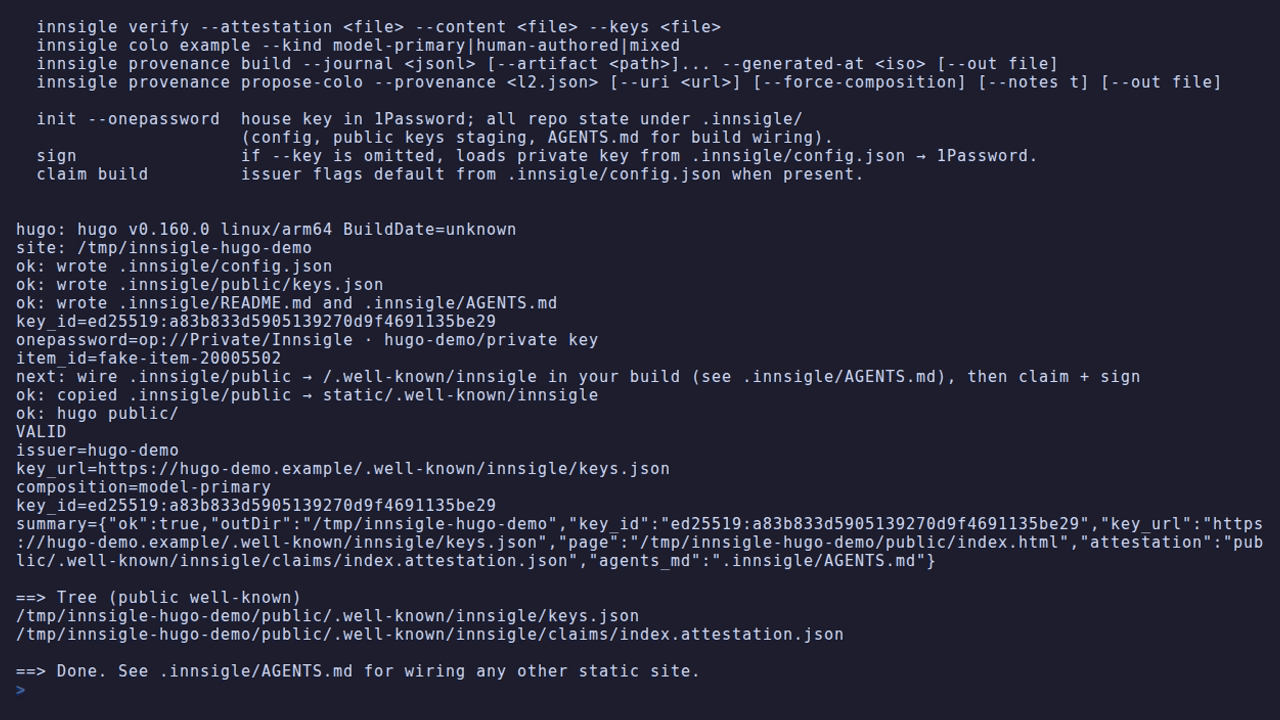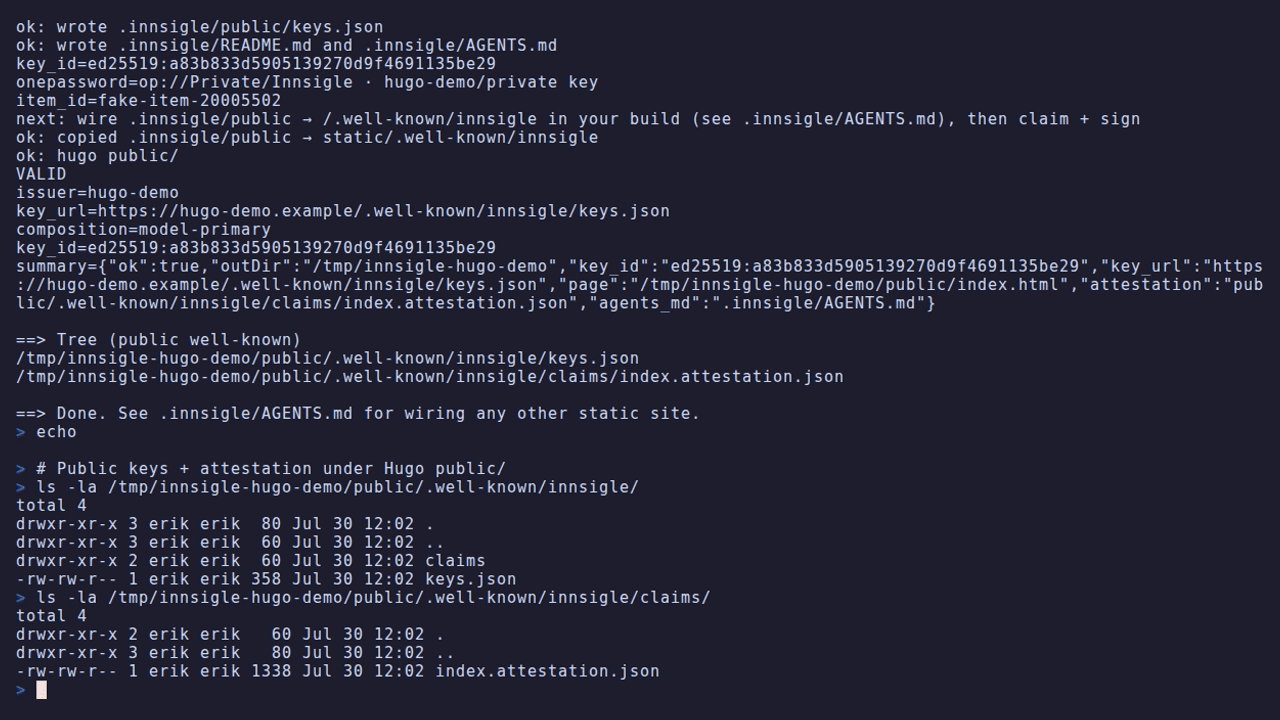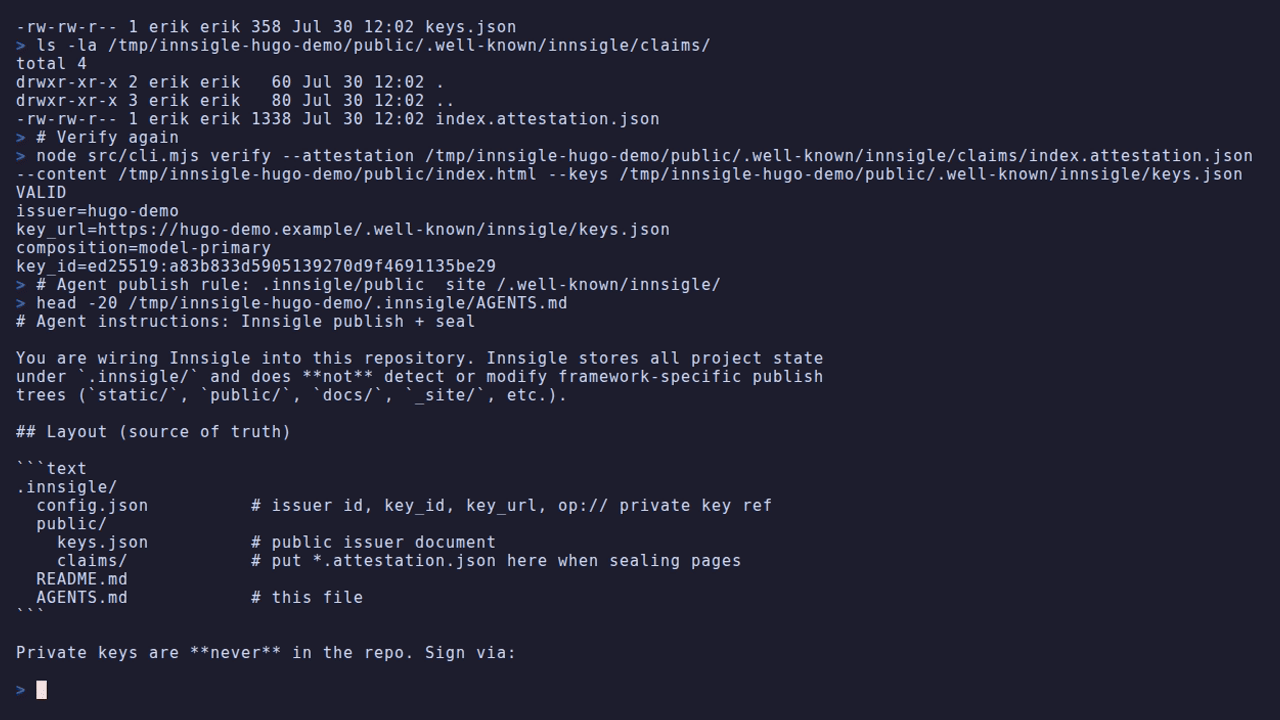
Step-by-step terminal walkthrough (narrated on screen):
- One-time
init→.innsigle/+ 1Password - Publish wire → copy public staging into the site
innsigle seal public/index.htmlinnsigle verify public/index.html→ VALID
Demo uses a stub op so recording does not need a vault; production uses op signin.
GIF fallback · regenerate with npm run record:hugo-walkthrough.
Goal
innsigle init --onepasswordwrites only.innsigle/- An agent (or you) copies
.innsigle/public/→ site/.well-known/innsigle/ - After
hugo,innsigle sealthe builtpublic/index.html innsigle verifyprints VALID
Prerequisites
- Node 20+
- Hugo on
PATH - 1Password CLI (
op) signed in
(e2e tests / screencast use a fake op via INNSIGLE_OP_BIN)
Automated proof (this repo)
npm test -- tests/hugo-workflow.test.mjs
# or:
node scripts/hugo-innsigle-workflow.mjs --out-dir /tmp/hugo-demo --keep
Expect: exit 0, stderr contains VALID.
Steps
1. Init (once per repo)
innsigle init --onepassword --site-url https://hugo-demo.exampleWrites .innsigle/config.json (fingerprint + op:// ref), stages .innsigle/public/keys.json, and AGENTS.md for publish wiring.
2. Publish wire (not Innsigle’s job)
mkdir -p static/.well-known/innsigle
cp -a .innsigle/public/. static/.well-known/innsigle/
3. Build, seal, verify
hugo -d public

innsigle seal public/index.html
innsigle verify public/index.html
# expect VALID
Optional: --kind model-primary|human-authored|mixed, or .innsigle/colo.json.
Re-run seal after rebuilds that change the published HTML bytes.
Check it
node scripts/hugo-innsigle-workflow.mjs --keep --out-dir /tmp/hugo-demoWhy Hugo is only an example
Innsigle never probes static/ vs public/ vs _site/. The same .innsigle/public → /.well-known/innsigle rule works for any static host — see .innsigle/AGENTS.md after init.
Spec
CONTRACT-001 · Issuer · CLI
 Innsigle seal: mixed by Innsigle (human key)
Signature covers the markdown source of this page, not these HTML bytes. This render quotes that seal.
- Composition
- mixed
- Issuer
- Innsigle
innsigle - Signing key
ed25519:15c6242b6ef825413847e221267959c9(human key)- Signed source
docs/website/content/curated/use/walkthrough-hugo.md- Signed
- 2026-09-30T20:46:37Z
- Content digest
sha256:2ba81ff0…c79d8a28
Human-controlled key. Signature is not a detector and not a truth guarantee.
Raw attestation JSON
{
  "payload": {
    "innsigle": "1",
    "type": "https://innsigle.dev/claim/colophon/v1",
    "issued_at": "2026-09-30T20:46:37Z",
    "issuer": {
      "id": "innsigle",
      "name": "Innsigle",
      "key_id": "ed25519:15c6242b6ef825413847e221267959c9",
      "key_url": "https://documentdrivendx.github.io/innsigle/.well-known/innsigle/keys.json"
    },
    "subjects": [
      {
        "uri": "https://documentdrivendx.github.io/innsigle/use/walkthrough-hugo/",
        "digest": {
          "alg": "sha256",
          "value": "2ba81ff01a715c6ecac70f03160e81b56e0bc74f6da15c25aa8954d1c79d8a28"
        }
      }
    ],
    "colophon": {
      "schema_version": "1",
      "composition": "mixed",
      "ingredients": [
        {
          "kind": "human",
          "name": "operator",
          "role": "outline"
        },
        {
          "kind": "model",
          "name": "Claude",
          "role": "expand"
        },
        {
          "kind": "human",
          "name": "operator",
          "role": "final-edit"
        }
      ],
      "notes": null
    }
  },
  "payload_encoding": "json",
  "signatures": [
    {
      "key_id": "ed25519:15c6242b6ef825413847e221267959c9",
      "alg": "ed25519",
      "sig": "zEdNfj5nLKvDsMq0lh9XNjrbTLXLEAJS-qWBYZMLccy7EQxX93MNQPmKWVE72q62K-piTB6SePQhz1A0yLF8AA",
      "signed_at": "2026-09-30T20:46:37Z"
    }
  ]
}